Highlights
- Fraud schemes are increasingly digitally enabled, networked, and difficult to investigate through disconnected systems.
- Modern fraud involves multiple deception layers with both internal and external actors exploiting organizational vulnerabilities.
- Effective fraud risk management requires balancing prevention, detection, and investigation with robust governance and controls.
Fraud schemes are becoming more digitally enabled, more networked and harder to investigate through disconnected systems alone.
For organizations under pressure to prevent losses, meet compliance expectations, and protect stakeholder trust, fraud risk management now depends on more than controls and training. It also requires the ability to connect data, identify relationships and turn suspicious activity into actionable investigative insight.
Consider a Minnesota small business whose trusted financial manager siphoned nearly , several years. What makes this case particularly instructive is the complexity of modern fraud—the employee herself was allegedly a victim of an elaborate online romance scam, demonstrating how today’s fraud often involves multiple layers of deception and both internal and external actors. This case serves as a powerful reminder that fraud risk can originate from inside or outside the organization—or both simultaneously—and highlights the critical importance of robust internal controls and regular audits in detecting suspicious activities before they escalate.
As this example demonstrates, organizations must understand that while individual actors remain common, sophisticated criminal networks with advanced digital capabilities are increasingly involved, often exploiting susceptible individuals to achieve their goals.
Jump to ↓
What is fraud risk?
Why managing risks is important
Understanding the fundamentals

White paper
Why you need an end-to-end solution for risk and fraud investigations
Access white paper ↗
What is fraud risk?
Fraud risk is the potential exposure of an organization to deceptive or dishonest actions, resulting in financial losses, reputational damage, or legal consequences.
To understand what fraud risk means, we need a clear understanding of what fraud is. Fraud involves intentional deception to gain something of value, usually money. One commits fraud through false statements, misrepresentation, or dishonest conduct intended to mislead or deceive. Fraud risk, then, refers to the possibility of financial loss due to the intentional deception perpetrated by an individual or a group either inside or outside the organization. In some cases, the perpetrators may be both internal and external.
Why does fraud occur?
Fraud occurs due to a combination of perceived opportunity, financial pressure, and rationalization, as described by the fraud triangle, wherein individuals exploit weaknesses in internal controls to commit deceptive acts.
Another way to ask the question is: Why does fraud risk exist? Either way, the answer might seem simple: People sometimes commit fraud because of greed or desperation. But that doesn’t explain why many avaricious or financially strapped individuals don’t engage in fraud.
A fuller explanation is provided by what’s called the fraud triangle. The fraud triangle is a model that’s used to describe the three elements that, when combined, are likely to lead to fraud. While fraud can be committed by a group of people, the fraud triangle’s explanatory power comes from the fact that fraud is typically initiated by an individual. Organizations seeking to undertake risk management—and all organizations should—need to understand the fraudster mindset.
Side 1: Pressure (or motive)
The “simple answer” may be incomplete, but it’s not necessarily wrong. A great deal of fraud is driven by greed or financial difficulty (such as gambling debts). But sometimes the motivation isn’t that simple. If the allegations are correct, the motive of the Minnesota woman charged with defrauding her company wasn’t personal financial gain. She was doing it for someone with whom she was romantically smitten.
Side 2: Opportunity
The fraudster needs access to money. In many cases, he or she oversees an organization’s funds as an accountant or a bookkeeper. That person typically writes checks and maintains the entity’s financial records. Such a person probably may not be managed or overseen closely. Perhaps the fraudster has a reputation for trustworthiness. Or perhaps the organization is so large and its records so complex that it’s difficult to detect fraudulent transactions.
Side 3: Rationalization
This may be the most fascinating and complicated side of the fraud triangle. Individuals who commit fraud typically don’t think of themselves as “bad people.” Perhaps they tell themselves, “I’ll pay it back just as soon as I can.” Or they might think, “Well, other people in the organization are using funds for their own benefit.” They often separate their fraudulent actions from the rest of their lives, reassuring themselves that, after all, they still go to church, give to charity, or spend quality time with their family. (Criminals in organized fraud gangs may simply think they have no legitimate alternatives.)
White paper
Why you need an end-to-end solution for risk and fraud investigations
Access white paper ↗Types of fraud
Fraud detection begins with an understanding of the types of fraud risk organizations face. Generally speaking, they can be distinguished as internal and external.
Internal fraud
As the term suggests, this is fraud committed by people within an organization. Some examples that any organization should beware of:
Accounting fraud involves deliberately falsifying financial statements and misappropriation of assets. This can be done in any number of ways, including overstating or understating revenue, assets, or expenses.
Mail fraud involves using the U.S. Postal Service to commit fraud. For instance, if someone mails a contract regarding a fraudulent deal, the government could pursue a fraud conviction against the person who sent it. Wire fraud is similar to mail fraud, except that non-postal transactions are used.
Check fraud involves creating counterfeit checks to defraud another. Someone may attempt to give a bad check to a bank to withdraw money that isn’t theirs.
Payroll fraud, which in some cases could be considered a form of accounting malfeasance, can take many forms: requests for fraudulent reimbursement, sales contracts that turn out not to be real, or paychecks for nonexistent employees.
Executive fraud occurs when executives in a business make false claims on financial statements to drive up its stock price or attract investors.
External fraud
Identity theft occurs when someone uses another person’s name, Social Security number, credit card number, or other personal information. This is done to open new accounts, make purchases, or take out loans. It is a common technique used by external bad actors pursuing one of the following types of fraud.
Bank fraud involves outsiders illegally obtaining money from a financial institution by any number of methods, most notably through false documents, forging signatures, or using stolen account information.
Insurance fraud occurs when the person lies or withholds information to obtain insurance benefits or coverage to which they’re not entitled. Techniques include using false identities, exaggerating the cost of damages, and faking injuries (which can include falsified medical documents).
Benefits fraud could be considered a kind of insurance fraud. Fraudsters will attempt to steal government benefits using false documents or false identities. They may also claim that they have a disability that makes it impossible for them to work.
Healthcare fraud could involve schemes related to pain management, insurance scams involving false documents or unnecessary treatments, and kickbacks.
Investment fraud occurs when investment fraudsters use false or misleading information to convince people to invest in a company or an investment strategy. The perpetrator may claim to have some secret knowledge or expertise, something that the “very wealthy” know that ordinary folks do not.
Many of these forms of fraud can also be instances of cyberfraud. The best-known examples are phishing and ransomware attacks. Cybercriminals are typically looking to lock up an organization’s IT system for ransom payments or to make off with its valuable data.
Some of these external forms of fraud can also be committed internally. Bank fraud is an obvious example, though an organization insider might also participate with an outsider in investment fraud or insurance fraud.
Modern fraud threats
Today’s fraud landscape is characterized by technological sophistication and global reach that previous generations of fraudsters could never achieve.
Synthetic identities
Digital technology is enabling individuals and fraud gangs to create synthetic identities–fake identities built upon real Social Security numbers or other purloined individual data. According to the McKinsey Institute, the use of synthetic identities is involved in about 85% of all fraud worldwide. This kind of identity fraud is expected to proliferate precipitously.
Artificial intelligence
Fraudsters can use artificial intelligence (AI) to more effectively create synthetic identities or more convincingly disguise themselves. But AI also can help organizations combat AI and safeguard their business. AI can analyze large data sets to identify patterns of behavior that may indicate fraudulent activities. Machine learning algorithms are developing predictive models that can identify which individuals or groups are more likely to commit fraud. AI also could be used in verifying customer or applicant identities.
Multi-channel criminal networks
With fraud becoming increasingly complex, fraudsters are operating within sophisticated networks that function across international borders. They also may collude with insiders and other digitally driven networks, which makes risk management and efforts for prevention, detection, and investigation more difficult.
Potential signs of fraud
While fraud risk is prevalent, it’s also worth noting that a great many fraudsters are detected. But it’s often several costly years before that happens. In most cases, organizations overlook red flags that might be signals of potential fraud. Red flags aren’t necessarily evidence of actual fraud. But they are examples of risk factors that an organization should be aware of–and investigate.
Insurers and financial services organizations need to be alert to signs of potential money laundering. Such red flags vary depending upon whether the potential perpetrator is a customer, broker, or vendor. Organizations required to comply with anti-money laundering (AML) regulations need to be especially vigilant.
Employee red flags include:
- Living beyond his or her means
- Financial difficulties
- Spending time in the office alone outside of work hours
- Remote work has made the detection of employee fraud more challenging
Management red flags include:
- Frequent disputes regarding risk audits
- A lack of transparency with employees about the organization’s financial performance
- Overly complex financial transactions
Why managing risks is important
Managing risks is crucial as it helps organizations anticipate, mitigate, and respond effectively to potential threats, safeguarding their assets, reputation, and sustainability in an ever-changing business environment.
All this means that organizations need to be able to manage fraud risk. Risk management is the process of identifying, assessing, and controlling potential risks or uncertainties that could negatively impact its objectives or finances. It helps organizations anticipate potential obstacles and reduce their impact, thus facilitating smoother operations, greater financial stability, and improved decision-making. In other words, risk management provides a roadmap for navigating potential risks in a proactive rather than reactive manner.
Risks are typically categorized as either operational risks or enterprise risks. Operational risks, which are risks associated with the execution of an organization’s operations, can originate from a variety of sources, including human error, third parties, or cybersecurity threats such as data breaches or ransomware attacks. Risk management professionals also identify technical risks associated with changes in technology and equipment. Technological advances can present new opportunities–and new opportunities for fraudulent behavior.
Benefits of risk management
Robust fraud risk management programs can provide numerous benefits, including:
- Reduced financial losses due to undetected fraud
- Reduced costs of responding to fraud (investigations, legal costs, etc.)
- More thorough regulatory compliance
- Improved employee sensitization to and awareness of fraud
- More effective corporate governance
Challenges of risk management
Effective fraud risk management isn’t simple to establish. Organizations need to be aware of risk management challenges and best practices.
Complexity and globalization
More and more fraudsters are operating within complex networks, many of which function across national borders. They also may collude with insiders and other digitally driven networks, which makes risk management and efforts for prevention, detection, and investigation more difficult.
Risk assessment
Risk assessment addresses relevant key areas pertaining to the organization’s size, complexity, industry, and goals. Effective fraud risk assessment should identify what types of fraud an organization is most susceptible to, where inside or outside the organization it could occur, and how it might be perpetrated. These fraud risks should then be prioritized based on their significance and likelihood. An organization should perform and update its risk assessment regularly to accommodate evolving fraud risks and the specific vulnerabilities that might arise.
Risk mitigation
Mitigation is a set of responses intended to reduce the harm of a risk event. Some forms of mitigation aim to prevent such an event. Others are intended to handle the event once it occurs. Most organizations can’t avoid every kind of fraud risk. But they can establish rules for handling them and minimizing their impact.
Establishing internal controls
Internal controls play a crucial role in minimizing fraud risk. Risk audits conducted by several parties across the organization (as well as by external auditors) can boost the effectiveness of fraud prevention, detection, and investigation efforts. These controls should be regularly reviewed and updated as needs change and new fraud risks arise.
Employee training
Education is an essential element of fraud prevention. An organization’s employees need to be able to recognize potential red flags as well as fraudulent emails and other forms of communication.
Understanding the fundamentals
To execute the process of risk management, organizations first need to understand its principles. They also need to find the right balance between these principles so that they’re using their resources efficiently and effectively.
Prevention
Fraud prevention, it should be obvious, is the best way to manage fraud risk. For government agencies, for instance, preventing fraud before it happens can be easier and certainly less costly in the long run than investigating and trying to claw back fraudulently obtained benefits.
Whatever the organization, fraud prevention is easier said than done. The reason why fraud often goes undetected for so long is trust. Few people want to believe that long-time employees, customers, or vendors might be capable of fraud. But accepting that possibility (however remote it might seem) is a necessary part of fraud prevention.
For those organizations involved in financial services, insurance, and government benefits, a key strategy is identity verification–ascertaining that customers, vendors, and benefits applicants are who they say they are. Following the risk management practices discussed above can help an organization create a vigorous culture of fraud prevention.
Detection
Fraud detection identifies activity that has occurred or been attempted. It responds to an existing threat. Detection methods tend to vary according to the type of fraud being committed. A great deal of financial fraud is due to manipulating accounting procedures. Fraud detection here requires auditors who know how to look for often hard-to-detect irregularities. For agencies managing government benefits, fraud detection often means giving application documents and related data painstaking scrutiny.
Today’s fraud detection increasingly relies on comprehensive data access and intelligent analytics. Professional investigation tools can help organizations identify patterns and connections that might indicate fraudulent activity by analyzing relationships between people, businesses, and assets across vast databases of public and proprietary records.
Investigation
Investigation begins once suspicious activity has been identified and requires organizations to examine financial records, identities, business relationships and other relevant data to determine whether fraud has occurred.
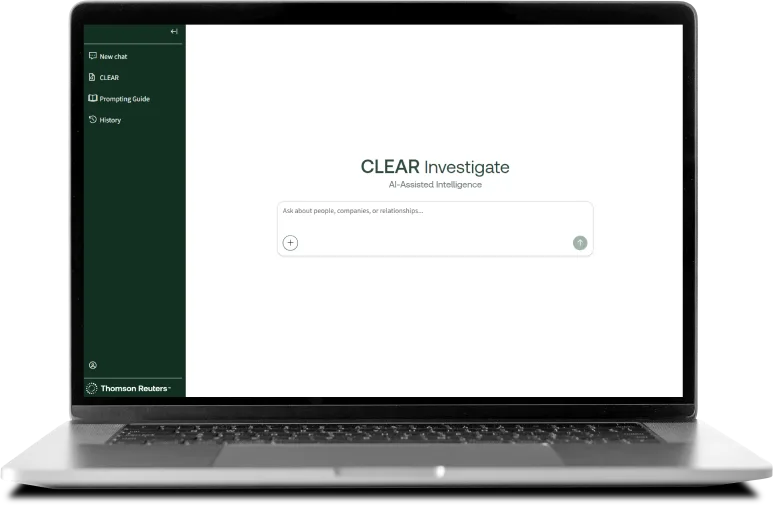
Modern investigation tools can help teams work more efficiently by bringing together trusted data, AI-powered investigative workflows and relationship analysis to surface relevant insights faster. Solutions such as CLEAR Investigate help investigators uncover unknown connections across people, businesses and assets, reducing time spent on manual research and supporting more informed, defensible outcomes.
Looking ahead
Fraud risk is not something organizations can solve once and move on from. As fraud schemes become more sophisticated, organizations need to balance prevention, detection and investigation with strong governance, internal controls and ongoing vigilance.
While technology will continue to play an important role, sustainable fraud risk management depends on combining trusted information, sound processes and experienced professionals who can adapt to an increasingly complex threat landscape. Those organizations that can do so will be better positioned to protect assets, maintain stakeholder trust and respond confidently when risks emerge.
Discover how CLEAR Investigate helps investigators uncover unknown connections, reduce manual research and bring forward relevant insights faster through AI-powered investigative workflows built on trusted data.
Access to these tools is limited to authorized, vetted professionals.
Thomson Reuters is not a consumer reporting agency and none of its services or the data contained therein constitute a “consumer report” as such term is defined in the Federal Fair Credit Reporting Act (FCRA), 15 U.S.C. sec. 1681 et seq. The data provided to you may not be used as a factor in consumer debt collection decisioning; establishing a consumer’s eligibility for credit, insurance, employment, government benefits, or housing; or for any other purpose authorized under the FCRA. By accessing one of our services, you agree not to use the service or data for any purpose authorized under the FCRA or in relation to taking an adverse action relating to a consumer application.